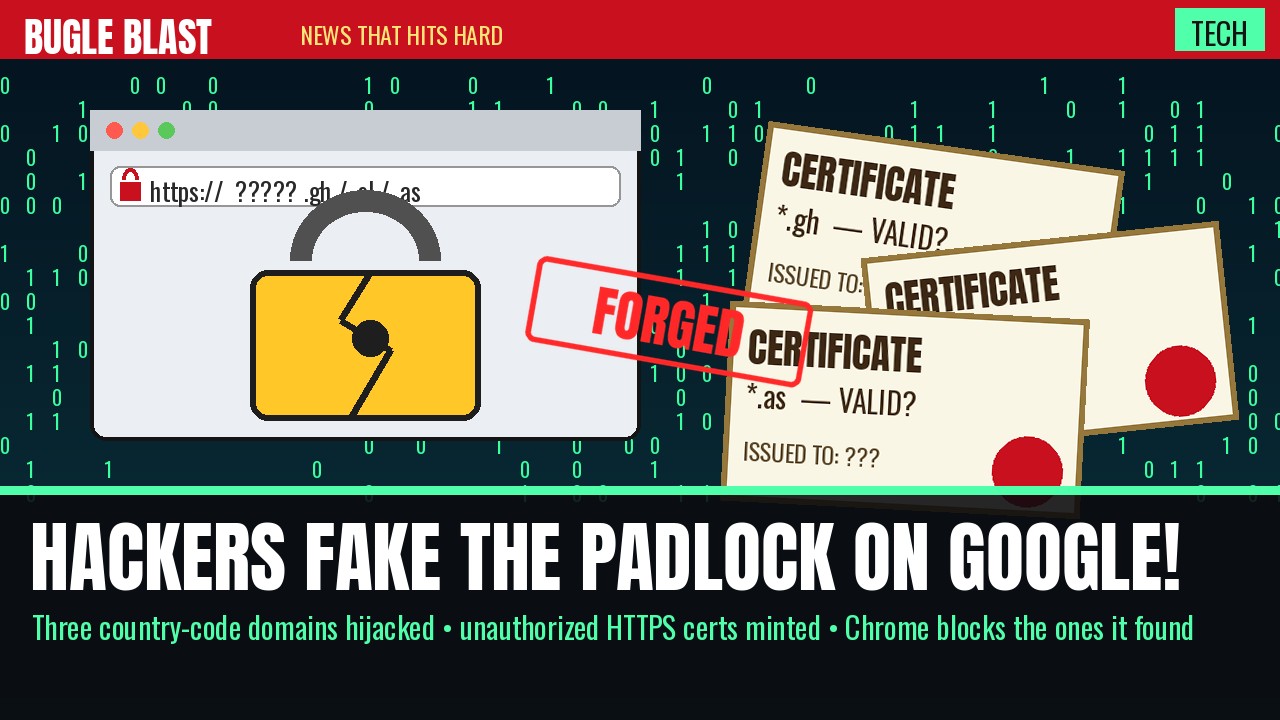
That little padlock in your browser? Somebody just counterfeited it. Google said Tuesday that attackers hijacked three country-code top-level domains — .gh (Ghana), .sl (Sierra Leone) and .as (American Samoa) — and used that control to obtain unauthorized HTTPS certificates covering “several Google domains” plus domains belonging to other organizations, according to Google’s own post.
How it worked: the attackers compromised the third-party ccTLD infrastructure and modified authoritative DNS records, Ars Technica explains. With traffic for selected sites pointed at them, they could pass the tests certificate authorities use to confirm someone controls a domain — and walk away with valid-looking certs. Google said its own systems were not compromised and it has “no reason to believe” the issuing CAs did anything wrong.
The fix so far: Chrome blocked the unauthorized certificates it identified using its emergency CRLSets mechanism, and Google worked with the issuing CAs to revoke them for other browsers. Google says Chrome users don’t need to do anything.
But here’s the gut punch, straight from Google: “Due to the complexity of DNS hijacks, we cannot guarantee that our analysis identified every affected domain, nor do Chrome interventions reliably protect non-Chrome users.” Google didn’t name the other affected brands, and Ars says it isn’t clear how many certificates were issued.
Got a website? Google’s advice is to watch Certificate Transparency logs for certs on your domains and publish restrictive CAA records naming which authorities may issue for you. History buffs will remember the 2011 DigiNotar hack, when forged Google certs were used against at least 300,000 people with ties to Iran, per Ars.
Sources: Google · Ars Technica
Leave a Reply